
Introduction to Stacktitan
StackTitan delivers expert-led cybersecurity assessment and advisory programs that help organizations understand how their defenses perform under real-world pressure.
exposing risk, testing controls, guiding remediation, and strengthening security posture over time.
Expert-led offensive security assessments combine human expertise, intelligent automation, and practical advisory services to identify real-world exposure across applications, cloud environments, infrastructure, identities, and complex attack paths. Every engagement delivers evidence of risk, practical remediation guidance, and measurable improvements in cyber resilience.
AI risk & exposure assessment
AI Risk & Exposure Assessments help organizations understand the risks introduced by AI platforms, cloud services, shadow AI usage, connected applications, and emerging attack techniques.
Sensitive data, business processes, and critical systems are assessed to identify practical exposure and prioritize remediation.
Penetration testing services

Application penetration testing
Expert-led testing identifies vulnerabilities across web applications, APIs, software platforms, and business logic to identify exploitable weaknesses before attackers can. The assessments uncover vulnerabilities that automated tools often miss, helping organizations reduce risk and strengthen application security throughout the development lifecycle.

Cloud penetration testing
Modern cloud environments introduce new opportunities for attackers to exploit misconfigurations, identity weaknesses, and exposed services. STACKTITAN evaluates cloud infrastructure, permissions, workloads, and attack paths to reveal how cloud risk can become business risk.

Network penetration testing
Network Penetration Testing evaluates internal and external environments to identify weaknesses, validate controls, and uncover the routes adversaries could use to gain access, escalate privileges, and move throughout the organization.

IoT/Hardware penetration testing
By assessing hardware, firmware, embedded systems, wireless communications, and connected ecosystems, STACKTITAN identifies vulnerabilities that could impact customers, operations, and business continuity.

Continuous penetration testing
Continuous penetration testing provides ongoing offensive security validation that helps organizations monitor exposure, verify remediation efforts, and understand how risk evolves as environments change.
Advanced offensive security services
Red team services
Real attackers do not follow a checklist.
STACKTITAN red team services emulate realistic adversary behavior to test how your people, processes, technologies, and controls perform under pressure. We:
- Simulate real-world attack scenarios
- Test detection and response capability
- Validate resilience against adversary behavior


Purple team services
Offensive and defensive security work better together.
STACKTITAN purple team services bring attackers and defenders into the same process to improve detection, response, remediation, and operational readiness.
- Connect offensive findings to defensive improvements
- Improve detection and response workflows
- Strengthen security operations through collaboration
vendor technology assurance
Organizations increasingly rely on third-party technologies to operate and grow.
STACKTITAN assesses vendor platforms, inherited systems, and third-party technologies to determine whether they are secure enough to trust.
- Evaluate third-party technology risk
- Validate security controls and assumptions
- Support procurement and governance decisions
Threat Hunting/Compromise Assessment
Compromise is not always detected when it happens.
STACKTITAN proactively searches across your environment for indicators of malicious activity, attacker persistence, and previously undetected breaches. We combine threat-led hunting with forensic analysis to determine whether compromise has occurred and identify the actions required to contain it.
- Uncover hidden attacker activity
- Validate whether systems have been compromised
- Support rapid containment and remediation
AI risk & exposure assessment
AI systems introduce new attack surfaces and new categories of organizational risk.
STACKTITAN assessments help organizations evaluate AI applications, cloud dependencies, shadow AI usage, and emerging threat models to strengthen governance and reduce exposure.
- Assess AI-related attack surfaces
- Identify data and access risks
- Support secure AI adoption
Maturity assessments
Understanding where your security program stands is essential for improving it.
STACKTITAN evaluates security capabilities, operational readiness, and governance maturity to identify gaps and prioritize practical next steps.
- Benchmark security capabilities
- Identify program weaknesses
- Create actionable improvement roadmaps
Research-based vulnerability discovery
Some security challenges require deeper investigation.
Using advanced research methodologies, reverse engineering, custom tooling, and specialist expertise, STACKTITAN uncovers vulnerabilities that conventional assessments may never find.
- Investigate complex systems
- Discover non-obvious vulnerabilities
- Support product and platform security
Attack path assessment
Business risk rarely exists in isolation.
STACKTITAN analyzes how weaknesses connect across systems, identities, permissions, applications, and infrastructure to create meaningful attack paths.
- Understand how attackers move
- Prioritize high-impact remediation
- Reduce pathways to compromise
Training
Technology alone cannot create resilience.
Our offensive security training programs help security, engineering, and technical teams understand attacker behavior, strengthen defensive practices, and improve operational readiness.
- Build offensive security awareness
- Improve team capability
- Strengthen security culture
CI/CD assessments
Modern software delivery depends on secure development pipelines.
STACKTITAN evaluates CI/CD environments, workflows, deployment processes, and access controls to identify weaknesses that could introduce risk into software delivery.
- Assess pipeline security
- Identify exposed secrets and permissions risks
- Improve software delivery resilience
Advanced offensive security services
Red team services
Real attackers do not follow a checklist.
STACKTITAN red team services emulate realistic adversary behavior to test how your people, processes, technologies, and controls perform under pressure.
- Simulate real-world attack scenarios
- Test detection and response capability
- Validate resilience against adversary behavior
Purple team services
Offensive and defensive security work better together.
STACKTITAN purple team services bring attackers and defenders into the same process to improve detection, response, remediation, and operational readiness.
- Connect offensive findings to defensive improvements
- Improve detection and response workflows
- Strengthen security operations through collaboration
vendor technology assurance
Organizations increasingly rely on third-party technologies to operate and grow.
STACKTITAN assesses vendor platforms, inherited systems, and third-party technologies to determine whether they are secure enough to trust.
- Evaluate third-party technology risk
- Validate security controls and assumptions
- Support procurement and governance decisions
Threat Hunting/Compromise Assessment
Compromise is not always detected when it happens.
STACKTITAN proactively searches across your environment for indicators of malicious activity, attacker persistence, and previously undetected breaches. We combine threat-led hunting with forensic analysis to determine whether compromise has occurred and identify the actions required to contain it.
- Uncover hidden attacker activity
- Validate whether systems have been compromised
- Support rapid containment and remediation
AI risk & exposure assessment
AI systems introduce new attack surfaces and new categories of organizational risk.
STACKTITAN assessments help organizations evaluate AI applications, cloud dependencies, shadow AI usage, and emerging threat models to strengthen governance and reduce exposure.
- Assess AI-related attack surfaces
- Identify data and access risks
- Support secure AI adoption
Maturity assessments
Understanding where your security program stands is essential for improving it.
STACKTITAN evaluates security capabilities, operational readiness, and governance maturity to identify gaps and prioritize practical next steps.
- Benchmark security capabilities
- Identify program weaknesses
- Create actionable improvement roadmaps
Research-based vulnerability discovery
Some security challenges require deeper investigation.
Using advanced research methodologies, reverse engineering, custom tooling, and specialist expertise, STACKTITAN uncovers vulnerabilities that conventional assessments may never find.
- Investigate complex systems
- Discover non-obvious vulnerabilities
- Support product and platform security
Attack path assessment
Business risk rarely exists in isolation.
STACKTITAN analyzes how weaknesses connect across systems, identities, permissions, applications, and infrastructure to create meaningful attack paths.
- Understand how attackers move
- Prioritize high-impact remediation
- Reduce pathways to compromise
Training
Technology alone cannot create resilience.
Our offensive security training programs help security, engineering, and technical teams understand attacker behavior, strengthen defensive practices, and improve operational readiness.
- Build offensive security awareness
- Improve team capability
- Strengthen security culture
CI/CD assessments
Modern software delivery depends on secure development pipelines.
STACKTITAN evaluates CI/CD environments, workflows, deployment processes, and access controls to identify weaknesses that could introduce risk into software delivery.
- Assess pipeline security
- Identify exposed secrets and permissions risks
- Improve software delivery resilience
managed offensive security services
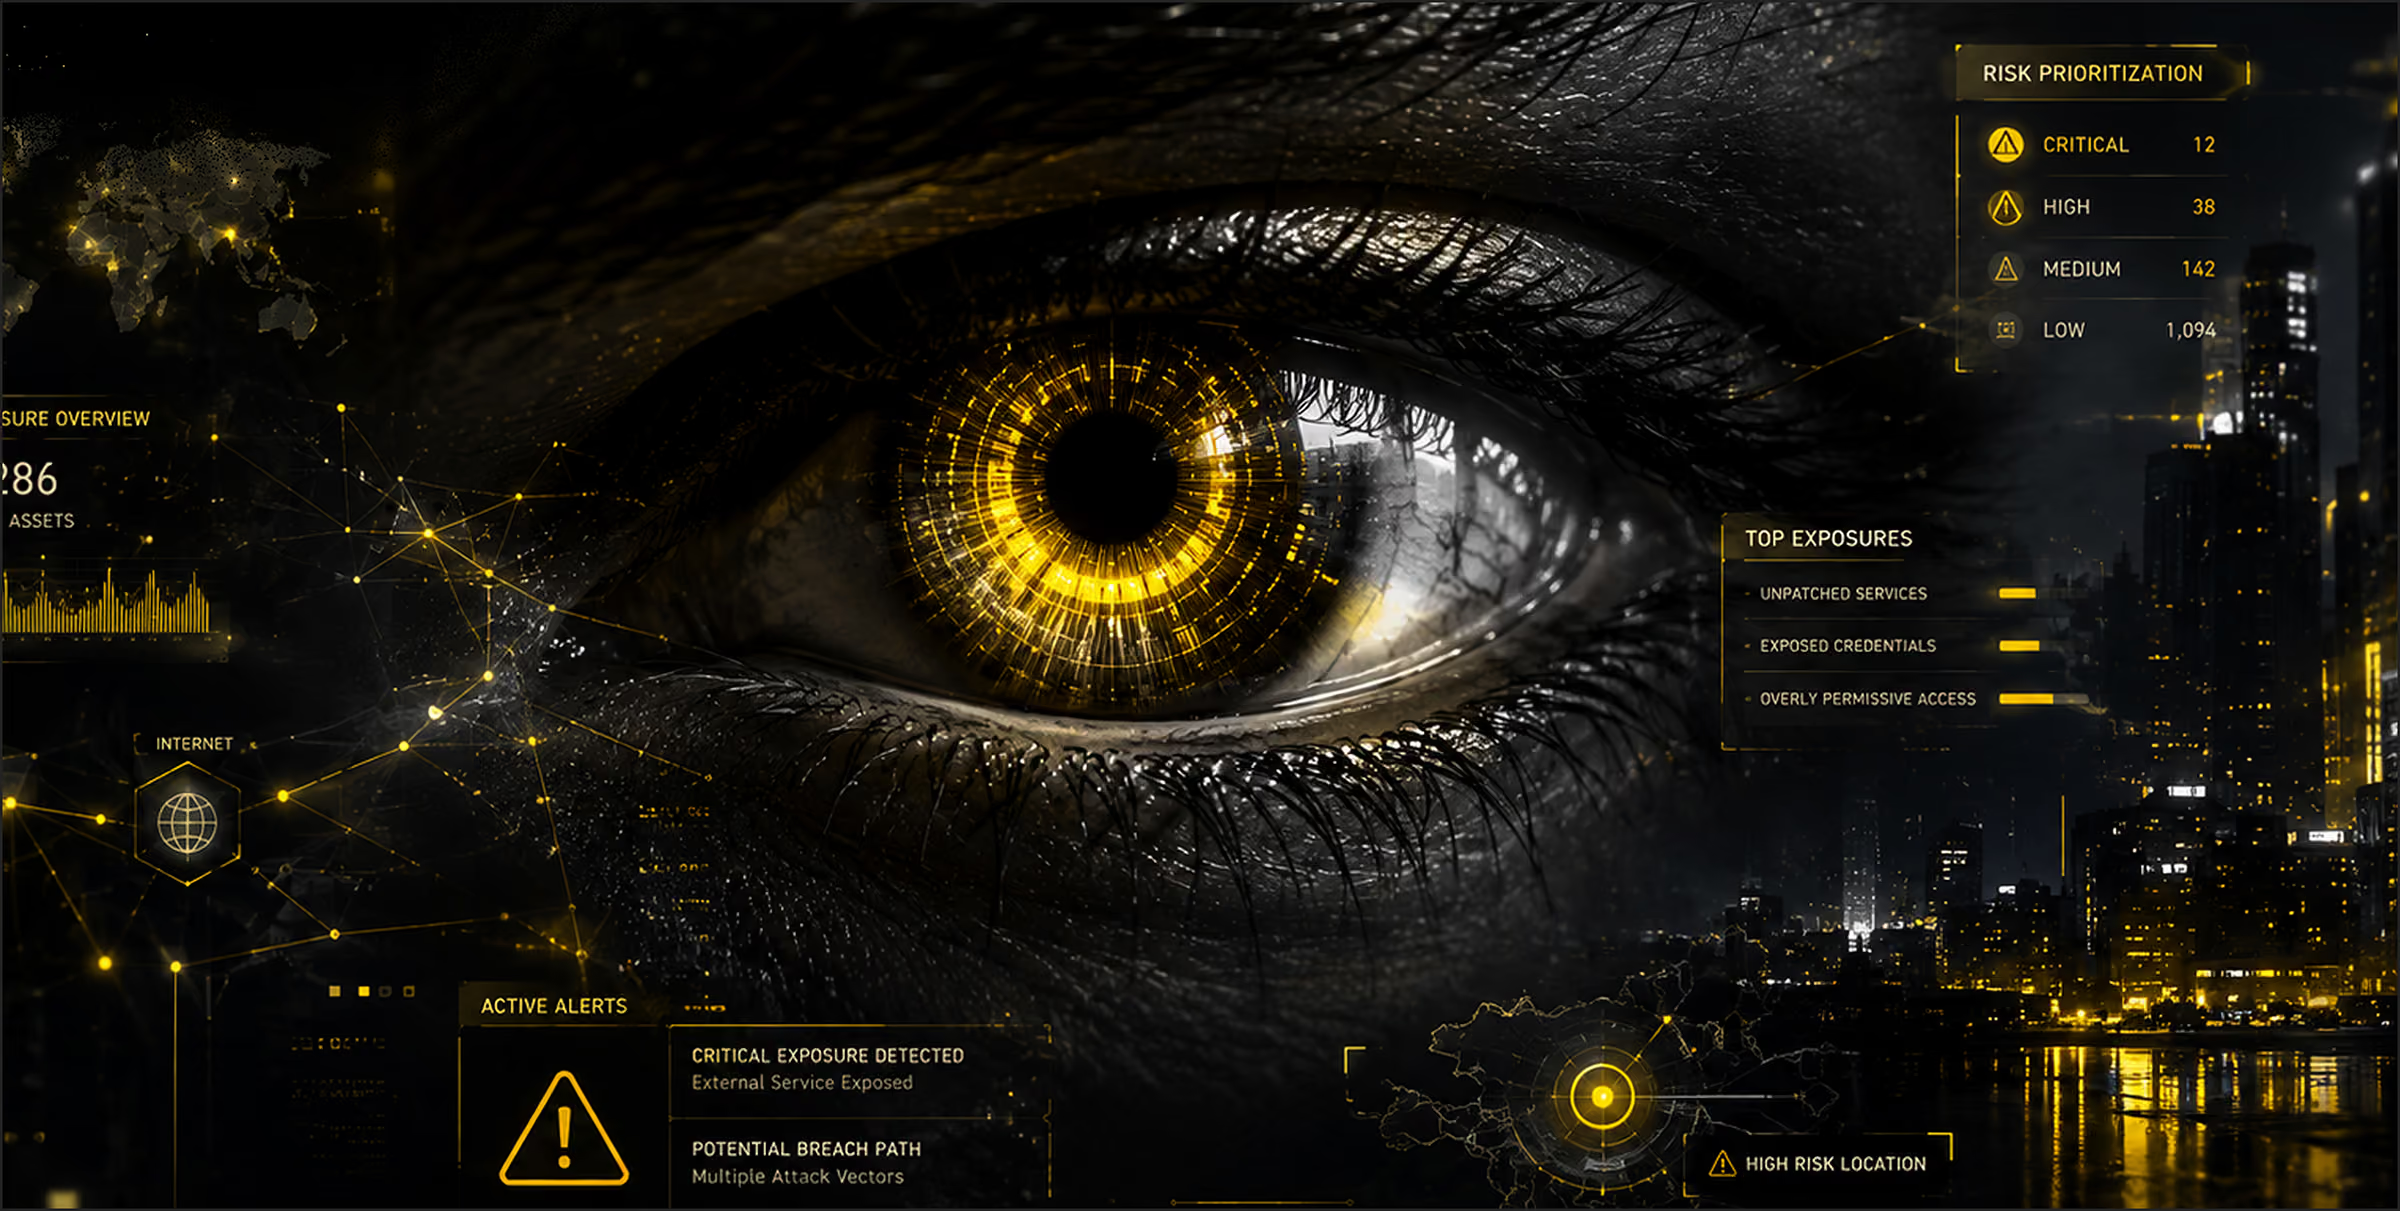
Continuous attack surface management
Attack surfaces are constantly changing.
Continuous Attack Surface Management helps organizations continuously identify, monitor, and prioritize exposed assets, vulnerabilities, and attack paths before adversaries can exploit them. STACKTITAN provides:
- Continuous visibility
- Exposure monitoring
- Risk prioritization
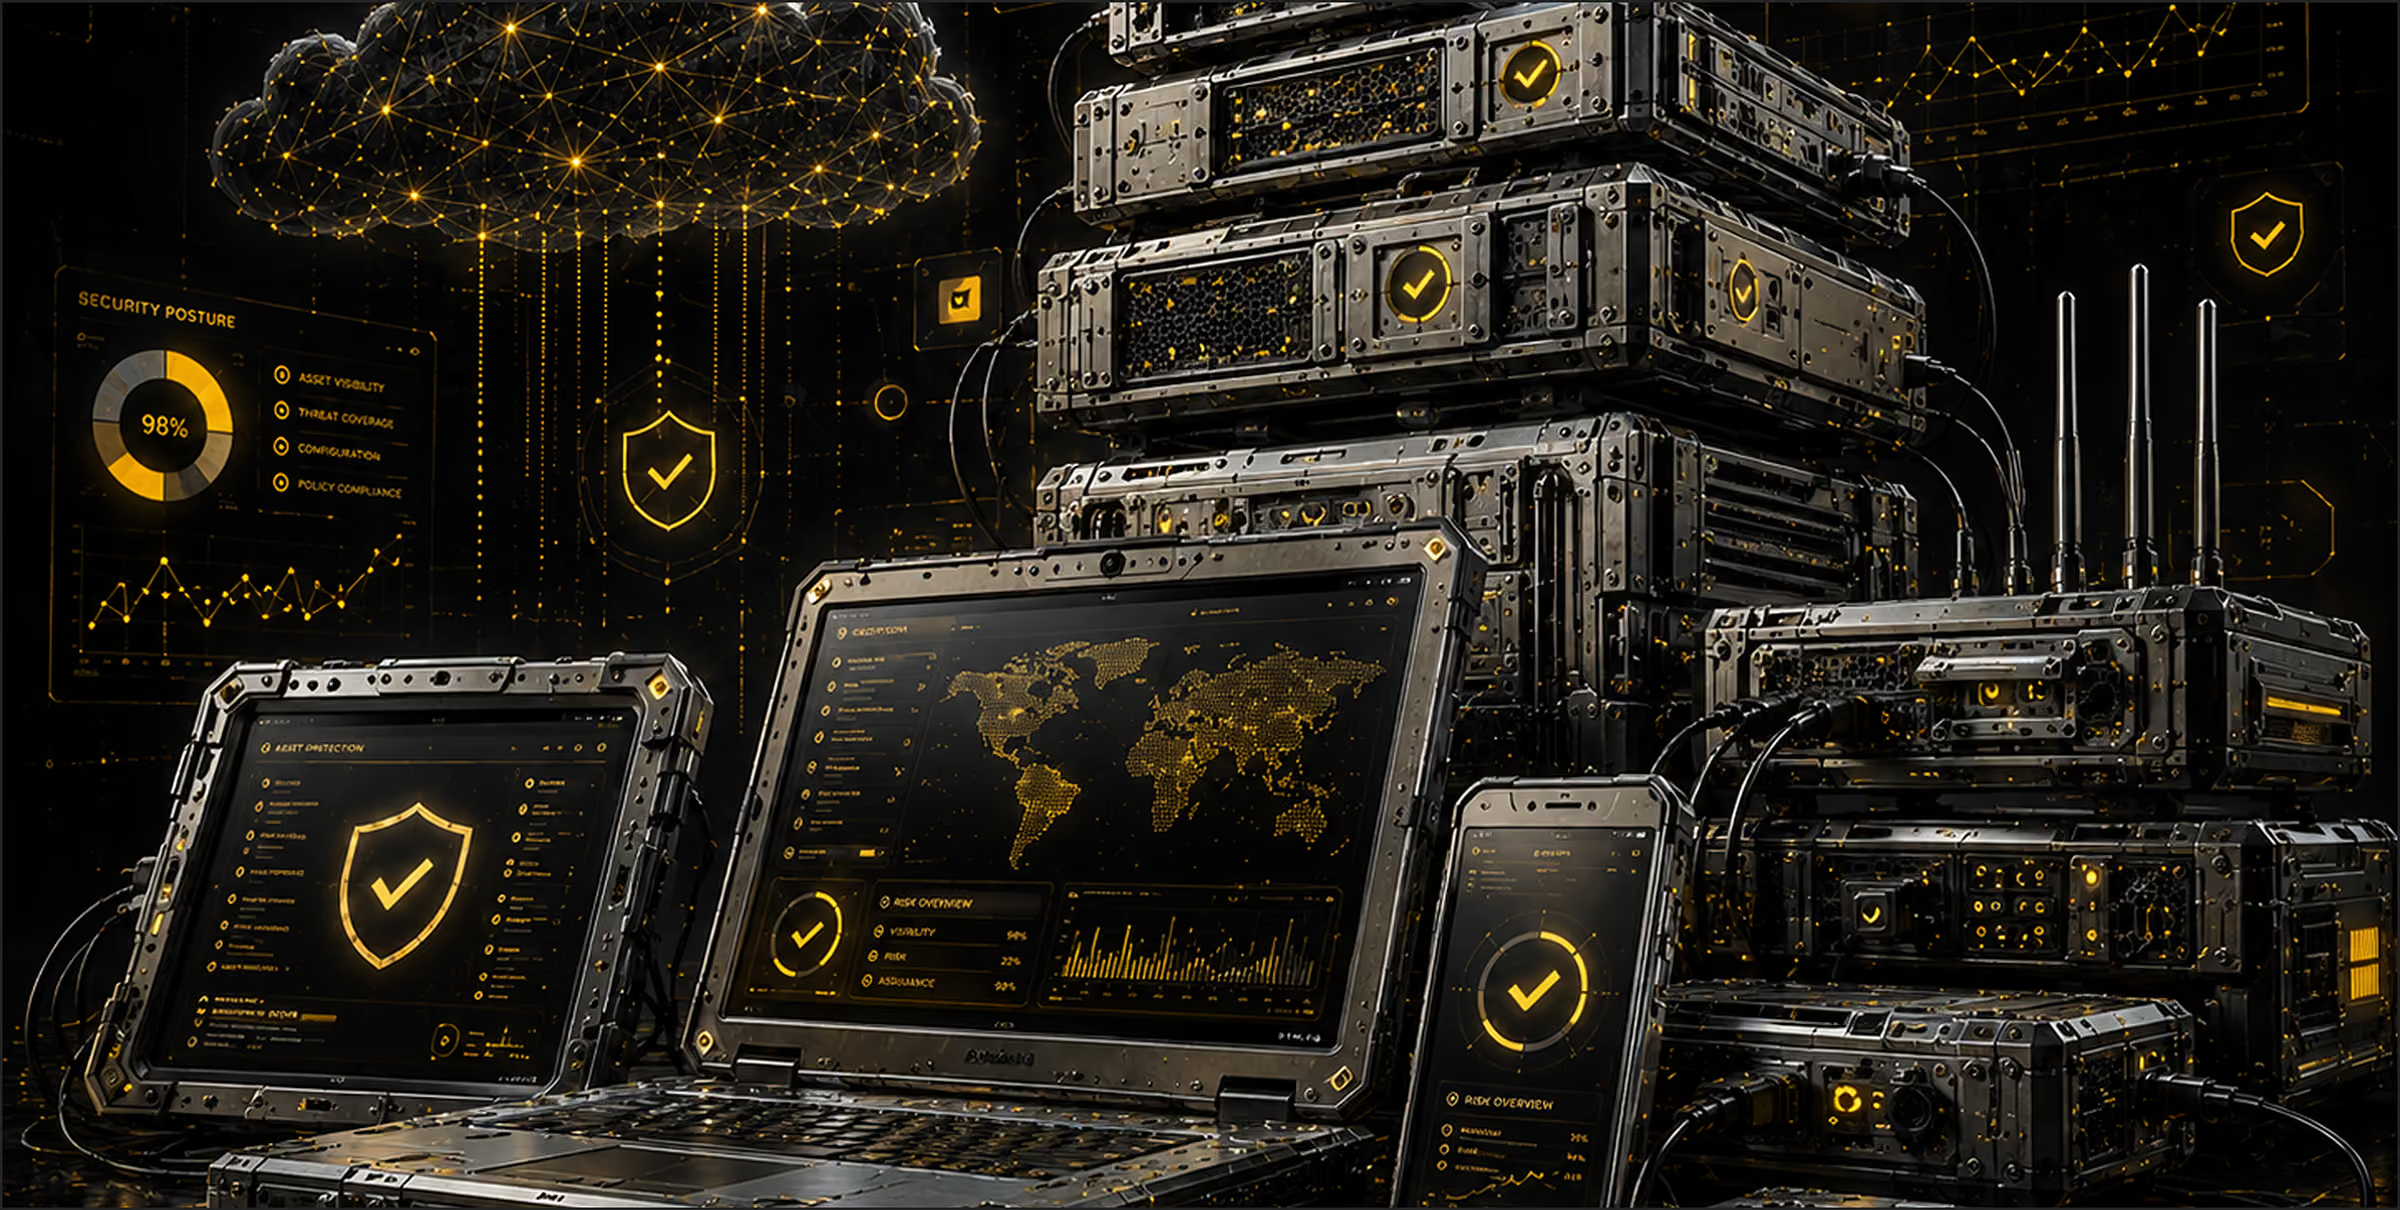
Managed device portfolio assurance
Organizations with connected products need ongoing assurance.
STACKTITAN helps manufacturers and technology companies continuously assess device portfolios, identify recurring security issues, and strengthen resilience throughout the product lifecycle. STACKTITAN delivers:
- Device security visibility
- Portfolio-level risk management
- Continuous assurance
Trusted by
Trusted by organizations where security is critical, STACKTITAN partners with enterprises across highly regulated and complex industries to validate risk, strengthen resilience, and protect the systems that matter most. From global brands to innovative technology providers, every engagement is focused on delivering measurable security outcomes.
THE STACKTITAN DIFFERENCE
Testing shaped around your environment:
Every engagement is adapted to your architecture, technologies, objectives and risk profile, ensuring the assessment focuses on the exposure that matters to your organization.
Proprietary technology extends assessment depth:
CEREBRAL, CLOUDHAWK and CANOPY give our experts additional visibility and insight beyond standard commercial security tools and testing practices.
Direct involvement from experienced leaders:
STACKTITAN’s founders remain closely involved in client engagements, bringing senior expertise, quality control and personal accountability to the work.
Support that continues beyond delivery:
We help your team interpret findings, establish remediation priorities and respond to questions after the formal assessment has finished.

